

Alert fatigue is overwhelming your team.
Too many tools generate too many alerts, burying critical threats in the noise.
Cyber threats in Australia are growing in scale, speed, and sophistication. Yet most organisations are still operating with siloed tools, alert fatigue, and security teams stretched beyond capacity.
The answer is not more tools. It's a unified, intelligent platform that brings your entire digital estate into view and responds at machine speed.
Too many tools generate too many alerts, burying critical threats in the noise.
On-premises, cloud, endpoints, and Saas tools don’t share signals. Attackers exploit the gaps.
Recruiting and retaining experienced security analysts is expensive and increasingly difficult.
Splunk and QRadar licensing, infrastructure, and maintenance costs are unsustainable at scale.
Give your security team complete visibility with AI-driven threat detection and automated response through Microsoft Sentinel.
Microsoft Sentinel is a cloud-native Security Information and Event Management (SIEM) and Security Orchestration, Automation, and Response (SOAR) platform. It ingests signals from across your entire digital estate (multi-cloud, on-premises, endpoints, and SaaS) and uses AI to detect, investigate, and respond to threats at scale.
Since 2025, Sentinel has been unified with Microsoft Defender XDR in a single Defender portal, giving security teams a consolidated console for SIEM and XDR capabilities. Microsoft was recognised as a Leader in the 2025 Gartner Magic Quadrant for SIEM.
Collect, detect, investigate, and respond to threats – all within a single unified platform, without the cost of managing separate SOAR infrastructure.
Built-in machine learning and Security Copilot integration surface threats faster than rule-based approaches, with explainable verdicts your team can act on.
Pay only for what you ingest, with commitment tiers offering up to 32% savings, and the new 50 GB tier making enterprise SIEM accessible for smaller organisations.
What can Microsoft Sentinel do for your organisation? These core capabilities make Sentinel crucial for defending against emerging threats:
Explore common use cases for Microsoft Sentinel that boost security operations and maintain compliance:
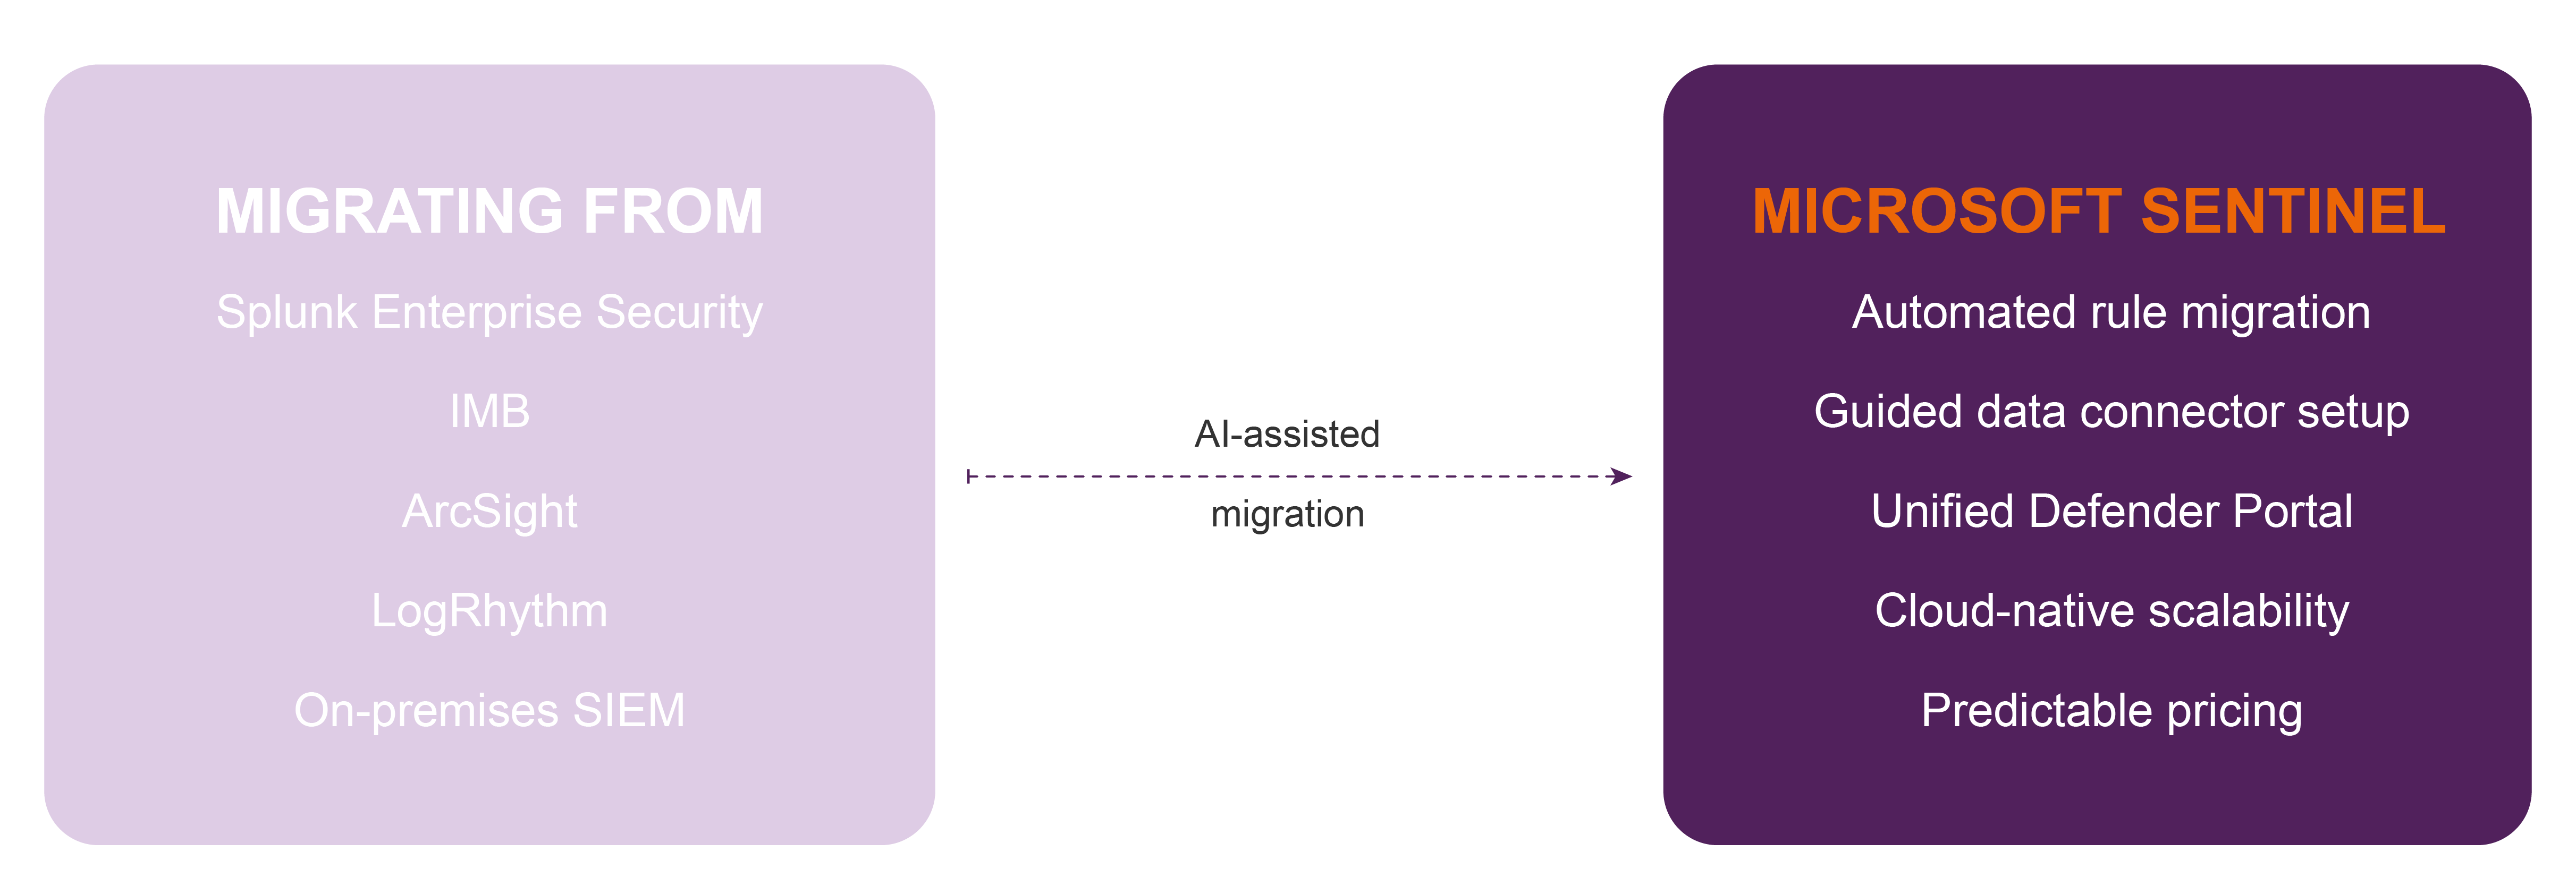
Microsoft's AI-assisted SIEM migration experience, combined with Professional Advantage's migration expertise, makes moving to Sentinel faster and lower-risk than ever before. Microsoft also offers free migration support through the Cloud Accelerate Factory program. Contact us to find out if your organisation qualifies.
We assess your current security posture, map your environment against the MITRE ATTACK Framework, identify coverage gaps and redundancies, and prioritise the use cases where Sentinel will deliver the greatest risk reduction for your organisation.
We design a Sentinel architecture tailored to your environment: selecting the right data sources, defining workspace and retention strategy, planning commitment tier and data lake usage, and mapping your automation and compliance requirements.
Our engineers deploy Microsoft Sentinel, configure data connectors (including legacy SIEM migrations from Splunk or QRadar), implement detection rules, build automated response playbooks, and integrate with your existing ticketing and workflow tools.
We act as an extension of your security team through our Modern Managed Services, providing continuous monitoring, rule tuning, playbook optimisation, incident escalation support, and monthly reporting on your security posture and SOC performance.
Professional Advantage combines Microsoft-certified security expertise with end-to-end delivery, helping Australian organisations not just deploy security tools, but actually stay secure. Unlike many Microsoft partners, mid-sized to large organisations choose to work with us for these reasons:
We hold Microsoft's Security specialisation, demonstrating verified capability in deploying Microsoft Sentinel, Microsoft Defender XDR, Microsoft Entra ID, and Microsoft Purview. Not all Microsoft partners are security specialists. We are.
We are uniquely positioned to support your entire Microsoft environment, from Sentinel and Defender to Microsoft 365, Azure, Entra ID, Purview, and Dynamics 365, under one partner. Add to that our Microsoft Tier 1 CSP capability, which means faster integrations, cleaner architecture, less complexity, and lower overall cost of ownership.
Since 1989, Professional Advantage has been helping Australian organisations navigate technology change. We understand the local regulatory landscape, including ASD Essential Eight, the Australian Privacy Act, and sector-specific compliance requirements.
Whether you have an established SOC that needs Sentinel expertise or a lean IT team that needs managed security coverage, we tailor our engagement model to your capability, acting as an integrated extension of your team, not an external vendor.
Since 1989, through every technology shift
World-class; most IT firms sit near 30
Most clients stay with us for the long run
AI Business Solutions
Dynamics 365, Power Platform, and Microsoft 365, including the Copilot and agent work built on top of them. Earned on delivered projects, certified people, and customer outcomes.
Security
Identity, threat protection, data security, and compliance across the Microsoft cloud, assessed on real security work delivered for Australian organisations.


Microsoft Sentinel is a cloud-native Security Information and Event Management (SIEM) and Security Orchestration Automated Response (SOAR) solution built on Microsoft Azure. It helps organisations detect, investigate, and respond to security threats across their digital environment.
What makes Sentinel a powerful solution?
Key Features
| Feature | What it does |
|---|---|
| Data Collection | Connects to Microsoft 365, Azure, AWS, on-premises servers, firewalls, and more. |
| AI-powered Threat Detection | Uses machine learning and Microsoft threat intelligence to identify real threats. |
| Investigation Tools | Visualise attack chains, timelines, and correlations across data sources with Auxiliary Logs and Analytics Logs. |
| Automated Threat Response | Trigger playbooks (via Logic Apps) to respond to incidents automatically. |
| Scalability | As a cloud-native tool, it scales automatically with your data and workloads. |
Learn more about Microsoft Sentinel in blog Modernising Security Operations with Microsoft Sentinel
Here’s a side-by-side comparison of the differences between Microsoft Sentinel and traditional SIEM solutions.
| Feature | Microsoft Sentinel | Traditional SIEM |
|---|---|---|
| Deployment | Cloud-native (built on Azure). | On-premises or hybrid. |
| Scalability | Auto-scales with data volume and users. | Requires manual hardware or license upgrades. |
| Setup & Maintenance | Minimal setup; no infrastructure to manage. | High setup and ongoing maintenance costs. |
| Integration | Seamless with Microsoft 365, Azure, Defender, and third-party tools. | Often requires manual connectors and integrations. |
| Cost Model | Pay-as-you-go based on data ingestion. | Typically fixed or tiered licensing with high upfront cost. |
| Artificial Intelligence | Built-in AI/ML for automated threat detection and correlation. | Often limited or requires separate modules. |
| Automation | Native SOAR via Logic Apps and playbooks. | Requires third-party tools or custom scripting. |
| Updates & Upgrades | Continuous updates via Azure platform. | Periodic manual upgrades needed. |
| Multi-Cloud Support | Supports Azure, AWS, GCP, and hybrid environments. | Typically fixed or tiered licensing with high upfront cost. |
| Time to Value | Fast to deploy and derive insights. | Slower setup; longer time to operationalise. |
In simple terms:
Yes. Sentinel can ingest data from Microsoft and third-party sources for unified SIEM and SOAR capabilities.
Popular third-party integrations with Microsoft Sentinel include, but are not limited to:
Security Solutions and Firewalls
|
Identity and Access Management
|
Email Security
|
Cloud Platform and SaaS
|
Endpoint Detection and Response (EDR)/XDR
|
Threat Intelligence
|
A standard Microsoft Sentinel deployment typically takes 4 to 12 weeks, depending on the size of your environment, the number of data sources, and the complexity of your detection and automation requirements.
Professional Advantage follows a structured methodology covering assessment, design, deployment, and handover, with ongoing managed services available post-deployment.
Microsoft Defender XDR is an endpoint-to-cloud detection and response platform focused on Microsoft's own security signals (endpoints, identities, email, cloud apps).
Microsoft Sentinel is a SIEM that ingests logs and signals from any source, including third-party tools like Cisco, AWS, Splunk, and SAP, and applies AI-driven analytics across your entire environment. Since 2025, both platforms have been unified in the Microsoft Defender portal, but they serve distinct, complementary roles. Most enterprise environments benefit from both. Learn more about Microsoft Sentinel in this article.
Yes. Microsoft Sentinel is a full-featured SIEM that can replace legacy platforms like Splunk and QRadar.
Microsoft now provides an AI-assisted SIEM migration experience that automates the migration of detection rules and data connectors, significantly reducing the effort required. Microsoft also offers free migration support through the Cloud Accelerate Factory program. Contact us to find out whether your organisation qualifies.
Professional Advantage can aid with end-to-end SIEM migration services, including rule translation, data onboarding, and team enablement. Sign up here for a commitment-free 1-hour consultation to learn how we can help.
Yes. Microsoft Sentinel has over 350 pre-built data connectors for third-party platforms, including Cisco, AWS, GCP, Palo Alto, Fortinet, SAP, Okta, and many more.
Its codeless connector platform allows custom integrations with virtually any data source. The connector ecosystem was significantly expanded at Microsoft Ignite 2025 and RSAC 2026 with new AWS, GCP, and DSPM integrations.
Yes. Microsoft Sentinel is now suitable for organisations of all sizes. The 50 GB/day commitment tier introduced in 2025 was specifically designed to make Sentinel more accessible and cost-predictable for smaller organisations.
Professional Advantage works with SMBs across Australia to right-size Sentinel deployments and provide managed services that fill SOC capability gaps without requiring a full in-house security team.
Whether you're assessing your security posture, planning a SIEM migration, or looking to get more from an existing Sentinel deployment, we can help. Book a free, no-obligation consultation with our team.
Contact us to speak to one of our experts today.

Cybersecurity Platform Consolidation, Essential Eight Compliance Services, Intune, Defender, Sentinel, Entra ID

Cloud and Application Support, Managed Security, End User Desktop, Server and Network Support

Microsoft 365 Copilot, Azure OpenAI, Power Platform Copilot, Dynamics 365 Copilot, Copilot Studio

Microsoft 365, SharePoint, iWorkplace Information Management and Compliance, Microsoft Purview
Check out how other organisations are successfully leveraging Microsoft’s security solutions.
Visit Case Studies


